LinuxCommandLibrary
GitHubF-DroidGoogle Play Store

apt-key

Deprecated APT key management utility for package authentication

TLDR

List the keys apt currently trusts
$ apt-key list
copy
Show the fingerprints of those keys
$ apt-key finger
copy
Add a key from a file
$ sudo apt-key add [path/to/key.asc]
copy
Add a key read from a pipe
$ curl -fsSL [https://example.com/key.asc] | sudo apt-key add -
copy
Fetch a key from a keyserver by ID
$ sudo apt-key adv --keyserver [keyserver.ubuntu.com] --recv-keys [key_id]
copy
Delete a key
$ sudo apt-key del [key_id]
copy
Export a single key
$ apt-key export [key_id]
copy
Export every trusted key
$ apt-key exportall
copy
Preferred today: give the repository its own keyring file
$ curl -fsSL [https://example.com/key.gpg] | sudo gpg --dearmor -o /usr/share/keyrings/[example].gpg
copy
Preferred today: bind one repository to that keyring with signed-by
$ echo "deb [signed-by=/usr/share/keyrings/[example].gpg] [https://repo.example.com] [stable] main" | sudo tee /etc/apt/sources.list.d/[example].list
copy

SYNOPSIS

apt-key [command] [arguments]

DESCRIPTION

apt-key is a deprecated key management utility for the APT Package Manager on Debian and Ubuntu. It manages the list of keys used by apt to authenticate packages.Note: apt-key is deprecated since Debian 11 (Bullseye) and Ubuntu 22.04 (Jammy). The recommended approach is to place keyring files directly in /etc/apt/trusted.gpg.d/ (with .gpg or .asc extension) or in /usr/share/keyrings/ and reference them via the `signed-by` option in sources.list entries. Only `apt-key del` remains supported for use in maintainer scripts.

PARAMETERS

list

List all trusted keys with fingerprints
add file
Add a new key to the list of trusted keys
del keyid
Remove a key from the list of trusted keys
adv
Pass advanced options to gpg
update
Update the local keyring with the archive keyring
net-update
Update the local keyring, fetching missing keys from a keyserver
export keyid
Output the key to standard output
exportall
Output all trusted keys to standard output
finger
List fingerprints of trusted keys (deprecated)
--keyring filename
Operate on a specific keyring file (deprecated)

CONFIGURATION

/etc/apt/trusted.gpg.d/

Directory for trusted keyring files in GPG format.
/usr/share/keyrings/
System-wide keyrings referenced via signed-by in sources.list.

INSTALL

sudo apt install apt
copy
sudo dnf install apt
copy
sudo pacman -S apt
copy
sudo apk add apt
copy
brew install apt
copy
nix profile install nixpkgs#apt
copy

CAVEATS

Deprecated in favor of placing keyring files directly in /etc/apt/trusted.gpg.d/ or using signed-by in apt sources. Only apt-key del should be used in maintainer scripts.

HISTORY

Part of the APT (Advanced Package Tool) suite. Deprecated starting with Debian 11 and Ubuntu 22.04 in favor of trusted.gpg.d directory.

SEE ALSO

apt(8), apt-get(8), gpg(1), apt-secure(8)
Braincup
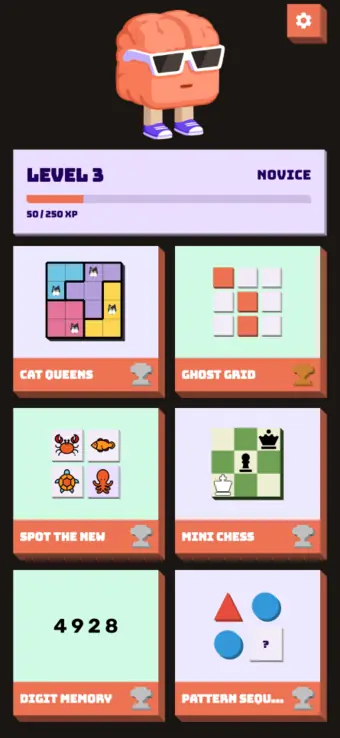
Open source brain training for math, memory and focus
Braincup mini-games
41 mini-games · Apache-2.0
No ads · No tracking
Play in browser
Download Braincup on the App StoreGet Braincup on Google PlayGet Braincup on F-Droid
276 stars
From the maker of Linux Command Library
Copied to clipboard
Braincup
Open source brain training for math, memory and focus. 41 mini-games, from mental arithmetic to Sudoku, N-Back and Solo Chess.
Apache-2.0 licensed · No ads · No tracking · No account
From the maker of Linux Command Library
Download Braincup on the App StoreGet Braincup on Google PlayGet Braincup on F-Droid